Orcher · Component 02 of 07

Role Identity Fabric

Binds the directive to a human and a role, cryptographically and revocably.

Layer 1 — sequential, gating

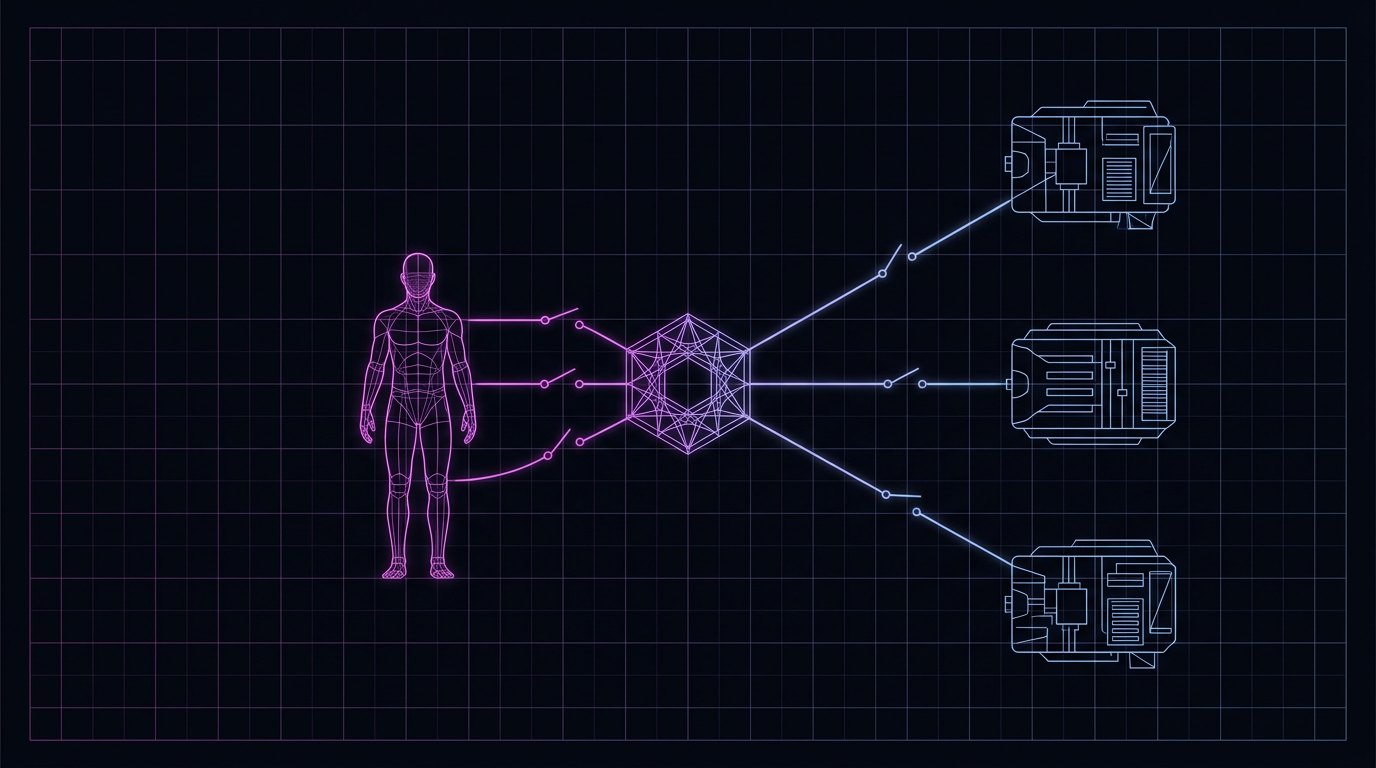
A named human bound by cryptographic filaments to the agents acting on their authority
Binds the directive to a human and a role, cryptographically and revocably.

Human-in-the-Role only means something if the role is enforceable. The Role Identity Fabric binds each directive to a named professional and the authority their role carries, then scopes the agent's permissions to that authority — not to a service account, not to a shared application identity, and not to a registry entry that merely records an agent exists.

  • Issues per-directive credentials bound to a human and their role.
  • Scopes permissions to the authority of that role, time-bound and task-bound.
  • Revokes authority instantly when a role changes, without redeploying agents.
  • Distinguishes agent identity from directive identity — a registry entry is not authorization.

Without it, agents borrow badges

Agents inherit broad service-account permissions and act with authority nobody granted them for this task. Registry sync tells you an agent exists; it does not stop it from acting outside a role at runtime.

What it emits

A role-bound authorization token attached to the directive for the life of the execution.

Evidence

Role Identity Fabric in the 2026 enterprise data#

Figures drawn from the Enterprise Superintelligence Report, Vol. I, August 2026.

144:1

non-human to human identities in the enterprise

up from 92:1 — Vol. I, p.11

92%

of organizations have no visibility into agent identities

Vol. I, p.6

86%

cannot enforce policy against those identities

Vol. I, p.6

14%

median role scope as a share of underlying account permissions

Vol. I, p.22

Vol. I · p.22Role-scoped authority across frontline, department head, and executive tiers

Mechanism

How it works#

Four stages, in order. Layer 1 components gate execution; Layer 2 components run continuously and never block.

  1. 01

    Resolve the human

    The directive is matched to an authenticated person in the enterprise identity provider — not to an application, a service principal, or a shared automation account.

  2. 02

    Resolve the role

    The person's role at the moment of the directive determines the authority available: what they may approve, up to what value, over which populations, in which jurisdictions.

  3. 03

    Mint per-directive credentials

    Orcher issues credentials scoped to this directive alone — task-bound, time-bound, and expiring on completion. Median role scope in deployment is about 14% of the underlying account's permissions.

  4. 04

    Enforce and revoke

    Every downstream call presents the role-bound token. A role change, suspension, or revocation invalidates authority instantly, with no agent redeployment and no waiting for a credential to age out.

Operational contract

Input
Signed directive plus enterprise identity assertion
Output
Role-bound authorization token attached to the directive
Mode
Layer 1 — sequential, gating
Scope
Task-bound and time-bound; expires with the execution cycle
Revocation
Immediate on role change; no redeployment required
Integrations
Enterprise IdP, HR system of record, and existing entitlement model

What it is not

It is not an agent registry

A registry records that an agent exists. It does not stop that agent from acting outside a role at runtime. The fabric binds authority, not inventory.

It is not a service account with better naming

Service accounts are static, shared, and over-permissioned by design. Per-directive credentials are none of those things.

Failure behaviour

If the human cannot be resolved, the role does not carry the required authority, or the entitlement is stale, the directive halts before any model call. There is no fallback identity to borrow.

Questions

What enterprises ask first

Do we have to replace our identity provider?
No. The fabric reads from the identity provider and HR system you already run. It adds directive-level scoping on top; it does not become your directory.
What happens when someone changes roles mid-execution?
In-flight authority is invalidated at the next gate. Work already verified and committed stays in the ledger with the role that authorized it at the time — which is exactly what an auditor needs to see.
How is agent identity different from directive identity?
Agent identity answers which process acted. Directive identity answers whose authority it acted under. Only the second is defensible when a decision is challenged.
Does this slow execution down?
Credential minting happens once per directive, before the first model call. The gate is measured in milliseconds, and it removes the far more expensive step of reconstructing authorization after the fact.

Where it shows up

Solutions and industries that depend on this

Surfaced automatically from the components each solution engages and each industry relies on.

The strategy behind the component

Dynamic model routing.#

Binding a platform to one heavy frontier model wastes tokens and leaks proprietary data. Dipp AI's strategy — and the reason Orcher's seven components exist — is intelligent routing: decouple orchestration from any single provider, match each task to the cheapest model that can carry it, and keep prompts and data inside the enterprise's own tenant boundary.

DIPP AI / ORCHER

Seven components. One enterprise-owned control plane.

01 + 02 / AUTHORITY

A role-bound directive

Intent, named professional, permitted actions and systems of record.

06 / COST GOVERNANCE

Dynamic model routing

Select the least costly sufficient model within the task’s stakes, latency target and spend ceiling.

Explore Cost Governance

05 / DATA CONTROL GATEWAY

Boundary before egress

Region, redaction, retention and training-exclusion requirements determine which destinations qualify.

Frontier reasoning

  • GPT-6 Astra
  • Claude Fable 5.1
  • Claude Mythos 5.1
  • Muse Spark 1.3

Models discussed in Dipp AI Research · September 6, 2026

Open-weight & private

  • Llama
  • Qwen
  • DeepSeek
  • Mistral
  • Gemma
  • Enterprise-tuned models

Model families · exact versions and licences assessed per deployment

Compute destinations

  • AWS
  • Microsoft Azure
  • Google Cloud
  • CoreWeave
  • Lambda
  • Crusoe
  • Private infrastructure

Hyperscalers, neoclouds and enterprise infrastructure

03 / Logic Scrubber

Verify proposed actions before commit.

04 / Immutable Audit Ledger

Preserve the decision and refusal evidence.

07 / Observability

Trace cost, latency and outcomes across routes.

Illustrative routing architecture, not a live connection status or an exhaustive integration catalogue. Provider availability, model access and deployment readiness are confirmed during a technical briefing.
01

Decoupled orchestration

Switch providers in a week, not a quarter.

An orchestration layer sits in front of every AI task rather than inside one vendor's SDK. Directives, roles, policy and evidence live in Orcher, so a provider change is a routing-table change — a week of work rather than a quarter of re-platforming — and no model vendor becomes the system of record for how the enterprise operates.

The protocol stack
02

Task-to-model matching

Roughly 90% of workloads never need the frontier.

Cost Governance routes by the stakes of the action rather than the habits of the developer. Standard, routine queries — roughly nine in ten workloads — go to cheaper open-weight or small in-house models; expensive frontier models are reserved for genuinely complex, high-reasoning tasks. Across 400-plus models and 70-plus providers the price spread is 4,500× (Vol. I, p.25), so the routing decision is the economics.

Cost Governance
03

Private tenant boundaries

Providers never learn from your interaction data.

The Data Control Gateway forces data and prompt histories to stay inside the company's own cloud environment — a private tenant, in-region — and verifies training exclusion and the data boundary on every call before a token leaves. Using frontier capability never means donating enterprise interaction data to the firm that sells it back.

Data Control Gateway

Runtime workflow

Authority per directive.#

Routing is not a developer preference resolved in a config file. For every directive, Orcher resolves who is accountable, selects the cheapest model class that authority permits, carries the data boundary along the chosen route, and hashes the whole decision into one evidence chain that reads the same across every provider.

  1. 01

    Authority is resolved before a model is chosen

    Who is accountable, and what may they authorize?

    The directive arrives with a named issuer. The Role Identity Fabric resolves that professional's current entitlements and binds them to this cycle, so the routing decision is made against a known authority rather than a service account. Anything outside the role halts here — before a single token is spent.

    Enforced by

    Emits
    A role-bound authorization token scoped to this directive.

  2. 02

    The routing decision is a policy decision

    What is the cheapest model class this directive's stakes permit?

    Cost Governance classifies the workload by stakes, sensitivity and reasoning depth, then selects the cheapest sufficient model class within the ceiling in force for that role. Roughly nine in ten workloads clear on routine classes; frontier capacity is reserved for complex work. The chosen class, the alternatives considered and the ceiling applied are all recorded as part of the decision.

    Enforced by

    Emits
    A signed routing decision: class chosen, ceiling applied, rationale.

  3. 03

    The data boundary travels with the route

    May this payload reach that provider, in that region?

    The Data Control Gateway applies data-boundary, redaction and training-exclusion rules to the route that was chosen, not to a default path. If a class is otherwise optimal but its provider cannot satisfy the boundary, the route is refused and the next sufficient class is selected. Consistency across providers is enforced by the gateway, not negotiated per vendor SDK.

    Enforced by

    Emits
    A per-call boundary attestation: region, redactions, no-training terms.

  4. 04

    Every decision lands in one evidence chain

    Can this be replayed and defended months later?

    The Immutable Audit Ledger hashes the directive, the authority, the routing decision, the boundary attestation and the committed action into a single tamper-evident chain. Observability streams the same run across whichever providers were involved, so one query answers what was asked, who authorized it, where it ran and what it cost — regardless of vendor.

    Enforced by

    Emits
    A replayable, hashed execution record with cross-provider cost and latency.

Proof points

The strategy, in measurable terms.#

Dynamic model routing is only a strategy if it moves numbers a finance team and an auditor both recognise. These are the outcomes it is accountable to.

Cost

4,500×

price spread across 400+ models and 70+ providers

The spread between the cheapest sufficient model and the frontier default is the entire economic case for routing. A directive sent to the wrong class does not fail — it just costs orders of magnitude more than it had to.

Vol. I, p.25

Token waste

~90%

of workloads never need a frontier model

Routine classification, extraction, summarisation and drafting clear on in-house or open-weight classes. Reserving frontier capacity for genuinely complex work is what turns AI spend from a run-rate into a budget.

Dipp AI routing model · Vol. I, p.25

Budget

68%

of enterprise AI programmes run over budget

Overrun is a control failure, not a forecasting failure. Cost Governance applies a ceiling per role and per directive and halts loops at the step boundary rather than at the invoice.

Vol. I, p.9

Latency

10×

faster on routine classes than a frontier default

Cheaper classes are also materially faster. Routing the routine nine-tenths off the frontier shortens the median directive as a side effect of the economics.

Indicative class latencies, Orcher routing table

Auditability

28%

of enterprises can trace an agent action end to end today

Every routing decision Orcher makes — class chosen, alternatives considered, ceiling applied, boundary attested — is hashed into the same evidence chain as the committed action, so the economics are as auditable as the outcome.

Vol. I, p.6

Portability

1 week

to change providers, not a quarter of re-platforming

Because orchestration is decoupled from any vendor SDK, a provider change is a routing-table change. Directives, roles, policy and evidence stay in Orcher.

Dipp AI protocol stack contract

The other six

Orcher is one control plane

Further reading · September 2026

The argument behind this page, published in full.

Two long-form pieces per week through September 2026 — sourced, dated, and attributed. Each one links back to the components it argues about.

Verified execution, or none at all.

Orcher is deployed with named enterprises under the Human-in-the-Role model. Request a technical briefing with the founding team.